When a team asks, does AI store prompts or use them for training, it is really asking several different questions. A provider may treat training, temporary processing, operational logging, human review, and long-term storage differently. A tool’s answer can also depend on the specific product, account type, model, and connected features.
That means a general privacy statement is not enough to make a decision about company data. Before staff submit confidential or regulated information, verify how the exact tool is configured and what its applicable terms say. The process below can help your business reach a clearer, documented answer.
Start with the exact AI product and account
First, identify the precise tool employees plan to use. Record the product name, account or subscription type, model, and any features that will connect it to company systems. These details matter because a free or personal account may have different controls or terms from a business subscription, API, enterprise deployment, or third-party assistant.
Include connected services in your review. An AI assistant that can search company files, access email, or send information to another application has a different data path from a standalone chat window. Confirm which services receive data and what permissions the connection uses.
If staff are already using the tool, ask them to identify how they sign in and whether they use personal or company-managed accounts. Do not assume that a company email address automatically places an account under business terms or administrator control.
Separate training from storage and access
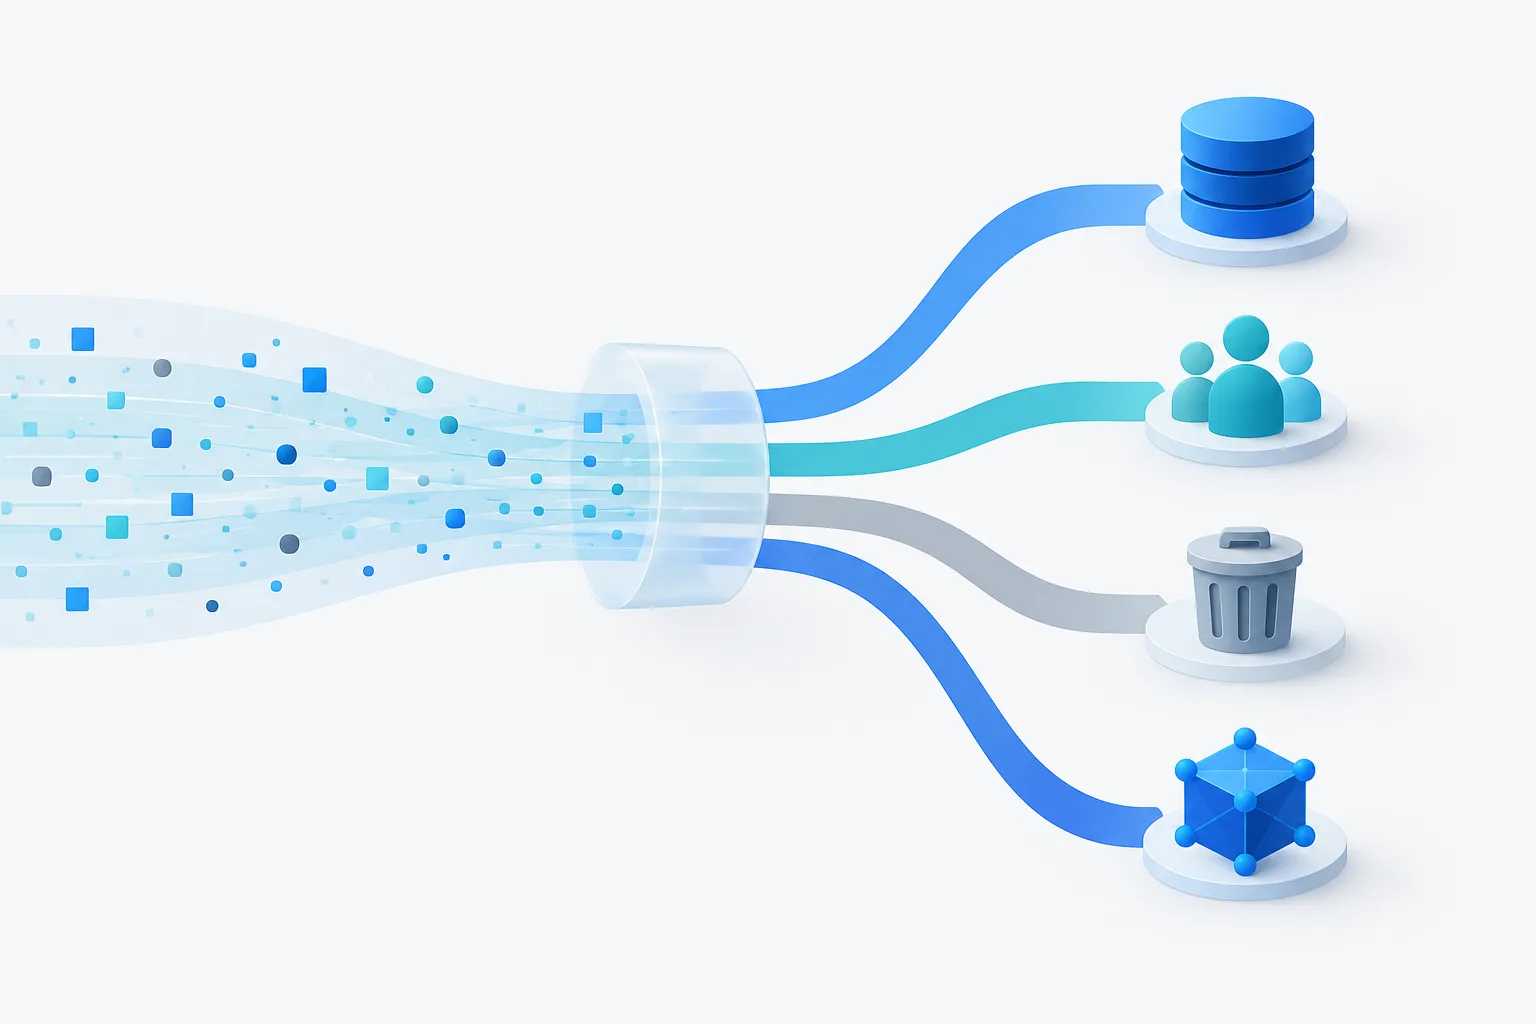
Ask the provider whether prompts, uploaded files, and generated responses are used to train or improve models. Then ask about storage separately. A statement that content is not used for training does not, by itself, explain whether the provider retains it in logs, keeps it for security or abuse monitoring, or allows it to remain in product history.
Check each kind of content individually. Prompts, attachments, generated responses, feedback submissions, and information retrieved through connected services may have different handling practices. Find out whether people can review any of that material, under what circumstances, and whether subprocessors receive it to operate or support the service.
For a practical example of how product-specific data controls can be documented, review Microsoft’s Copilot privacy information. Use the provider’s documentation for the exact product your organization uses rather than assuming another product follows the same practices.
Check settings, terms, and supporting documents
Review the service’s settings and its written terms together. A setting can describe a configurable option, while the contract or data-processing terms explain the provider’s commitments and responsibilities. Neither should be treated as a substitute for checking the other.
- Administrator controls: Look for settings related to model improvement, data sharing, conversation history, feedback, retention, and connected applications. Confirm whether an administrator controls them or whether individual users can change them.
- Default behavior: Check whether each setting is enabled by default, applies to all users, and covers the model and features your staff will use. Record the current configuration and who is responsible for maintaining it.
- Retention terms: Find out how long prompts, files, responses, and logs are kept. Ask whether retention varies by feature, account type, or support and security processes.
- Deletion process: Confirm who can request deletion, how to submit a request, what it covers, and whether copies in backups or with subprocessors are included. Ask what happens when an account is closed or a user deletes a conversation.
- Contract documents: Review the applicable business terms and any data-processing addendum. Make sure the documents match the account and product being considered, rather than relying on terms for a different service tier.
For API services, a provider may document data controls separately from the consumer-facing product. For example, OpenAI’s platform data controls documentation describes controls for its API platform. Check the relevant documentation for your provider and deployment, and verify whether a setting applies to the specific data and feature at issue.
Get unclear answers in writing
If the documentation does not answer a question, contact the provider and keep the response with your vendor records. Ask direct, specific questions rather than relying on broad assurances:
- Are prompts, uploaded files, and responses used to train or improve models?
- What information is retained, for what purposes, and for how long?
- Can provider personnel review content, and under what circumstances?
- Which subprocessors or connected services receive business content?
- Can an administrator configure retention or training-related settings for all users?
- How can the organization request deletion, and what data does deletion cover?
- Do the business terms differ from the free or personal-use terms?
Save the provider’s written answers, the relevant terms, and a record of your settings. Revisit them when the product, subscription, model, connected services, or provider terms change. A review process makes it easier to notice when the original decision no longer reflects how the tool is being used.
Pause before using regulated or confidential information
Before entering regulated or highly sensitive information, verify that the product, account, configuration, and contract are appropriate for that specific use. A general privacy statement alone does not establish that a tool is suitable for every kind of business data.
Healthcare organizations handling electronic protected health information should specifically assess business associate agreement requirements and confirm applicable safeguards before using a provider to process that information. Have the appropriate compliance lead or qualified advisor review the arrangement. The NIST Generative AI Profile can also help organizations frame a broader review of generative AI risks and controls.
Until the review is complete, set clear boundaries for staff. They can use approved tools and permitted information while the organization assesses whether more sensitive content is appropriate. This is not a substitute for evaluating the provider, but it helps avoid treating an unverified tool as approved for every task.
Make the decision part of vendor management
Keep a simple record of the product reviewed, its account type, relevant settings, applicable terms, provider answers, approved data uses, and the person responsible for follow-up. Share the outcome with employees in plain language so they know which tool to use and what information they may enter.
This review fits into a broader process for evaluating technology vendors and aligning tools with business needs. Zevonix provides IT consulting and strategy, as well as compliance support that includes HIPAA and GDPR. You can read more about reviewing and optimizing IT vendors or strategic technology planning for Florida businesses.
Frequently asked questions
If a provider does not train on business data, can it still store prompts?
Yes, those are separate issues to verify. Check the provider’s retention and logging practices, including how long it keeps prompts, files, and responses and whether they are used for purposes such as security or service operation.
Where should I look for data-sharing and training settings?
Start with the product’s privacy or data-control settings and its administrator console, if available. Then compare the settings with the terms and data-processing documents that apply to your exact account and product.
Can a business administrator control retention or request deletion?
That depends on the provider and service. Ask whether administrators can set retention limits, who can submit a deletion request, and whether deletion includes backups, logs, and data held by subprocessors.
What should a business verify before using AI with regulated data?
Confirm the exact product and account, applicable contracts, retention and access practices, administrator controls, and required safeguards. For ePHI, specifically assess whether a BAA is required and in place before use.
Conclusion
To find out whether an AI tool stores prompts or uses them for training, verify the exact product and account, inspect its settings and terms, and ask for written answers about retention, access, sharing, and deletion. For help aligning AI use with broader technology and compliance planning, contact Zevonix to discuss your organization’s needs.